The 24-Hour Cyber Clock Has Started: Can You Prove What You Knew, When You Knew It — and What You Did?
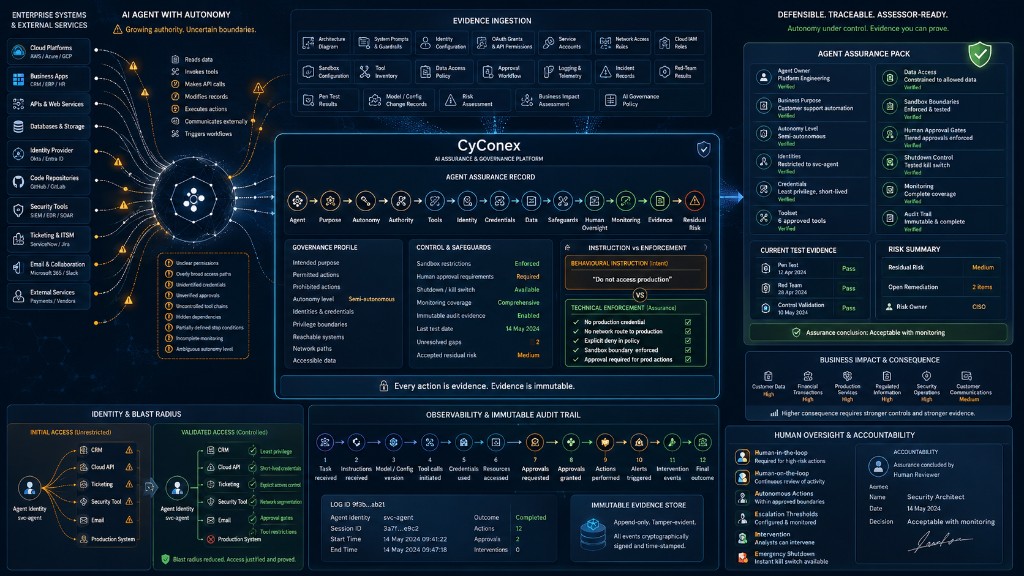
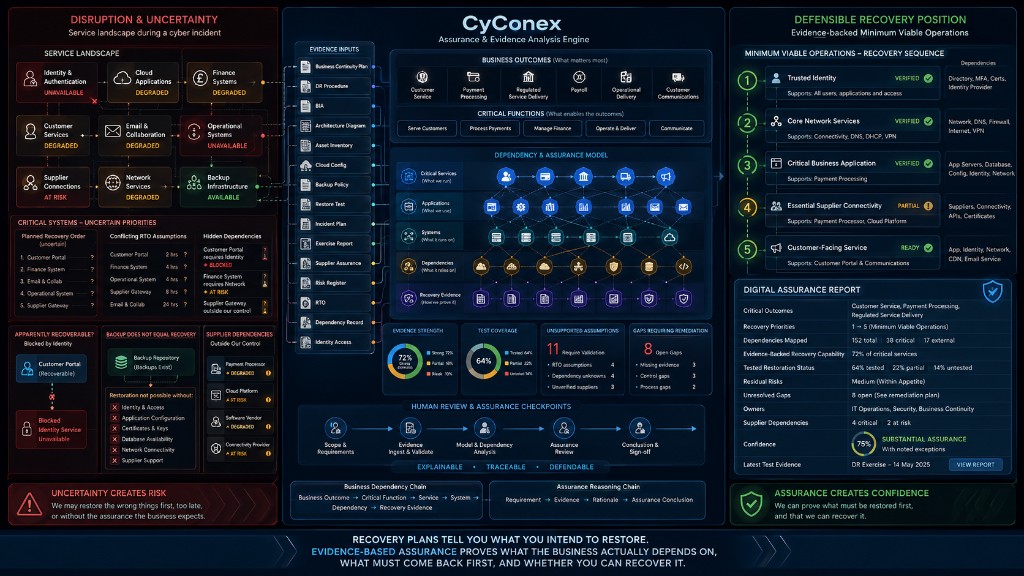
Cyber regulation is beginning to measure organisations in hours rather than audit cycles. This article explains why incident response plans alone cannot meet 24-hour reporting clocks, why evidence relationships and provenance matter, and how decision-ready assurance turns evidence into a defensible answer before the clock runs out.
Read more